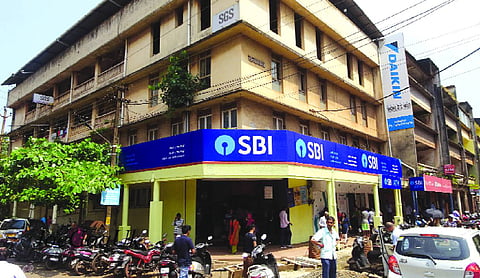
The State Bank of India (SBI) on Wednesday announced that hackers breached and exposed personal dataof some customers , including mobile numbers, addresses, loan details, and other sensitive information such as branch and Customer Information File (CIF) identifiers. The bank received alerts on October 16 from its threat intelligence service provider, the Defence Cyber Agency and CERT-In.
CERT-In also announced on Wednesday that private keys associated with Indian digital certification authority eMudhra and its certificates have been compromised. eMudhra certificates verify trusted digital assets and ensure secure online data transmission. The cyber security watchdog added that the breach at eMudhra Ltd compromise of private keys linked to eight intermediate CA certificates in its public key infrastructure, including six TLS certificates and two code-signing certificates.
“Some social media accounts indulging in fear mongering about its impact. Reported security incident pertains to global certificate biz, impact on Indian sites very limited. Digital signature certificates, eSign services is regulated by Controller of Certifying Authorities remain unaffected,” IT Ministry said on eMudhra incident. The ministry has formed a special team to probe the matter
The two major cyber security incidents follows a critical advisory by CERT-In last week, warning that autonomous AI agents accessed live systems and confidential data of Indian organisations without authorisation.
In filings with stock exchanges, SBI said that it suspected exposure of 3,897 customer records containing personally identifiable information on the dark web. The filing said the incident has had no material impact on the bank’s core business operations, financial performance, or business continuity, and that its core business functions continued to operate normally without disruption. A detailed assessment is underway, and the bank is implementing appropriate remedial and preventive measures, it said.
According to the bank, a preliminary analysis of about 3,75,000 records found on the dark web identified 3,897 customer records. The exposed information reportedly included customers’ registered mobile numbers, dates of birth, names, gender, email addresses, residential addresses, branch and CIF identifiers, lead IDs, and details linked to loan records. The bank says it does not yet know where the data came from and has engaged a CERT-In-empanelled agency to lead the investigation.
SBI added that it was closely monitoring the situation and taking all appropriate measures in accordance with applicable regulatory requirements. The bank also said it needed a detailed investigation to establish the authenticity and completeness of the exposed data, determine the potential source and extent of the exposure, and assess the associated risks to customers and the bank.
In a social media post, SBI said the incident has impacted a small number of customers. “Customer balances are completely safe, and we are taking all possible steps to protect the interest of our valued customers,” it said
The disclosure comes amid increasing cybersecurity risks faced by institutions in critical sectors, with concerns compounded by the ability of Artificial Intelligence (AI) systems to further exploit security loopholes.